Master the first 6 core foundation modules of CEHv12 alongside real-world Web Application Penetration Testing & Bug Bounty Hunting. Taught by certified security researchers at VHASS Softwares Pvt. Ltd. with hands-on Kali attack ranges, guaranteed internship opportunities, and lifetime recordings.
Trained Engineers
Verified Student Rating
Virtual Attack Labs
Salary Potential
Accredited by VHASS Softwares Private Limited
Click any operational attack scenario below to launch live simulated commands in our Kali Linux virtual sandbox. Witness how real security engineers recon, exploit, and report vulnerabilities.
Structured step-by-step from core networking fundamentals and attacker mindset, progressing to system exploitation and high-paying web bug hunting.
Understand core concepts like IP, TCP/UDP, OSI layers, ports, and protocols—essential for hacking any system. Master packet structures, subnetting, DNS, and traffic routing mechanisms.
Develop a hacker’s mindset: think creatively, question everything, and always explore the “what if?” Learn attack vectors, threat modeling, and how offensive security researchers break trust assumptions.
Learn about ethical hacking concepts, attacker types, cyber warfare, and the comprehensive phases of a cyberattack (Recon, Scanning, Gaining Access, Maintaining Access, Clearing Tracks).
Discover how to gather information passively and actively using Open Source Intelligence (OSINT), search engines, social engineering reconnaissance, DNS records, and automated tools.
Identify live hosts, open ports, and running services using industry-grade network scanning tools and techniques. Master stealth SYN scans, UDP scans, banner grabbing, and firewall evasion.
Extract detailed, actionable information about systems, such as valid usernames, network shares, SNMP queries, LDAP directories, and services, from an isolated target network.
Learn to identify, verify, and prioritize software vulnerabilities using enterprise scanners like Nessus, OpenVAS, and Nikto. Understand CVSS scoring, CVE databases, and false positive reduction.
Dive deep into gaining access, privilege escalation, maintaining persistent control, password cracking, steganography, and covering tracks like seasoned penetration testers.
Understand the economics and rules of bug hunting on HackerOne, Bugcrowd, and Intigriti. Master program scopes, rules of engagement, legal safe harbors, and vulnerability reward expectations.
Setup your high-performance offensive web hacking workstation. Configure Burp Suite Professional, CA certificates, browser profiles, FoxyProxy, Docker labs (DVWA, PortSwigger Web Academy, Juice Shop).
Uncover hidden attack surfaces: Subdomain enumeration, ASN discovery, cloud bucket hunting, JavaScript file analysis, secret extraction, hidden parameters, and content brute-forcing.
Master the HTTP/HTTPS request-response architecture, session cookies, JWT authentication, CORS policies, API endpoints (REST & GraphQL), and common client-server communication flaws.
Deep dive into exploitation: SQL Injection (SQLi), Cross-Site Scripting (Reflected, Stored, DOM XSS), Insecure Direct Object References (IDOR), SSRF, CSRF, and critical Business Logic vulnerabilities.
Supercharge your hunting efficiency. Automate routine workflows using Bash pipelines, Python exploit scripts, Nuclei custom YAML templates, and continuous target recon notifications.
Writing reports that get accepted and paid out. Learn CVSS calculation, proof-of-concept (PoC) preparation, communicating with triage teams, handling duplicate disputes, and maximizing bounty payouts.
Indian students deserve practical, verifiable training—not outdated PowerPoint theory. Here is how VHASS Academy guarantees career acceleration, industry credibility, and financial return on investment.
Cybersecurity professionals in India command 2.5x higher entry compensation compared to generic software engineering. Here is your expected salary trajectory after completing the CEHv12 + Bug Bounty program:
Awarded officially through VHASS Softwares Private Limited (Government Registered Corporate Entity).
Top performing students receive direct corporate internship placements with VHASS Softwares Pvt. Ltd. and cybersecurity consulting partner networks.
No endless theoretical slides. Every module involves executing real attacks inside isolated Docker containers, vulnerable target servers, and web applications.
Get your doubts cleared in real-time by certified security researchers through our exclusive private student WhatsApp batch community.
| Evaluation Feature | VHASS ACADEMY (Cohort 2026) | Traditional Generic Institutes |
|---|---|---|
| Curriculum Depth | Dual-Track: CEHv12 Core 1-6 + Live Web App Bug Bounty | Outdated slides, no real web bug hunting |
| Practical Execution | 100% Virtual Kali Attack Range & Dockerized Targets | Theory lectures & pre-recorded outdated videos |
| Certification Authority | ISO 9001:2015 Accredited & Verifiable Online | Generic internal certificate with no accreditation |
| Corporate Internship | Direct Project Guarantee with VHASS Softwares Pvt. Ltd. | No practical work experience provided |
| Community & Mentorship | 24/7 Official WhatsApp Batch Community with Instructors | Support tickets that take days to respond |
| Investment Fee | ₹4,999 (All-Inclusive Subsidized Pass) | ₹35,000 – ₹75,000 with additional lab costs |
Single comprehensive enrollment covering both CEHv12 Core & Bug Bounty Tracks with all benefits included.
Complete certification bundle offered by VHASS ACADEMY
Got questions about the batch, requirements, or certification? Find your answers below.
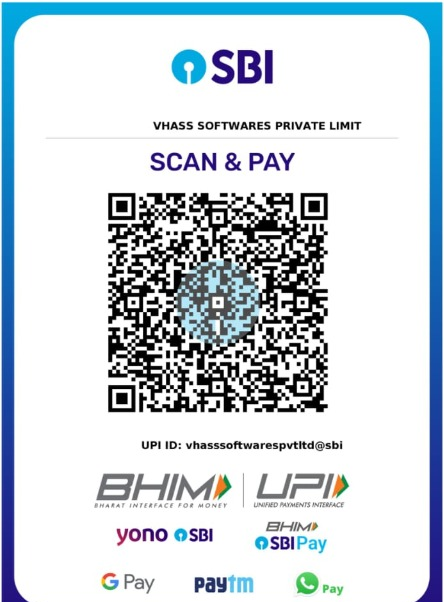
vhasssoftwarespvtltd@sbi
After scanning and paying via UPI, enter the 12-digit UPI Reference / UTR Number from your payment receipt (e.g. 429184719283):
Please do not refresh or close this browser window.
Welcome to VHASS ACADEMY. Your registration and seat are securely reserved!